


Free Sep-2026 UPDATED Fortinet NSE5_FNC_AD_7.6 Exam Questions & Answer
Latest Success Metrics For Actual NSE5_FNC_AD_7.6 Exam Realistic Dumps
NEW QUESTION # 14
An organization has FortiNAC-F deployed and is using Layer 3 isolation networks across multiple sites with firewalls. At a minimum, which three protocols must be allowed between the isolation networks and FortiNAC-F? (Choose three.)
- A. NTP
- B. DNS
- C. HTTP/HTTPS
- D. DHCP
- E. DDNS
Answer: B,C,D
Explanation:
The correct answers are C, D, and E . In a Layer 3 captive or isolation network design, FortiNAC-F port2 acts as the captive network service interface. The study guide states that Layer 3 captive networks require DHCP traffic to be relayed to port2 from the captive networks, and that the FortiNAC-F interface provides DHCP, DNS, and captive portal services to hosts assigned to any captive network.
That means the firewall path between the isolation VLANs and FortiNAC-F must allow DHCP , so isolated endpoints can receive an IP address from the FortiNAC-F captive network scope; DNS , so the isolated endpoint uses FortiNAC-F as its DNS server and gets redirected correctly; and HTTP/HTTPS , so the endpoint can load the FortiNAC-F captive portal page. The guide's browser-redirection flow confirms this sequence: the host is moved to the isolation VLAN, requests DHCP, receives FortiNAC-F as the DNS server, performs DNS lookup, and then Apache/Tomcat services present the portal content.
Option A , DDNS, is not required for captive portal operation. Option B , NTP, may be useful for endpoint time accuracy or certificate-related workflows, but it is not part of the minimum traffic required for FortiNAC- F isolation network operation.
NEW QUESTION # 15
As part of a FortiNAC-F integration with FortiGate for management of VPN users, what must be configured on FortiGate to keep FortiNAC-F up to date with VPN session information?
- A. SNMP traps
- B. RADIUS accounting
- C. Syslog messages
- D. Security Fabric integration
Answer: C
Explanation:
The correct answer is D . For FortiGate VPN integration, FortiNAC-F depends on syslog from FortiGate to receive VPN user, IP address, and session information. The FortiNAC-F study guide states that after a remote user successfully authenticates and establishes a VPN connection, FortiGate sends user, IP, and session information to FortiNAC-F using syslog. This keeps FortiNAC-F aware of the VPN session so it can apply the correct access control state and update FortiGate when the device becomes trusted.
Option A is wrong because SNMP traps are commonly used for infrastructure events, link traps, or third-party event inputs, but this VPN workflow uses FortiGate syslog. Option B is wrong because RADIUS accounting can update session information in some NAC workflows, but the FortiGate VPN integration described in the guide uses syslog. Option C is wrong because Security Fabric integration is not the required mechanism for keeping FortiNAC-F updated with VPN session details in this scenario.
NEW QUESTION # 16
An administrator has created several device profiling rules and evaluated all existing devices in the database.
Some of the devices appear in the profiled devices view because they matched a rule, but they remain unknown and the registration column in the profiled devices view shows " No " .
What is the most likely cause?
- A. The devices match more than one device profiling rule.
- B. The device profiling rule has registration set to manual.
- C. The confirm device profiling rule option is not enabled.
- D. The devices have persistent agents installed, and the point of connection has PA optimization enabled.
Answer: C
Explanation:
In FortiNAC-F,Device Profiling Rulesare used to automatically identify and categorize devices (such as IP cameras, printers, or IoT devices) based on fingerprints like DHCP fingerprints, OIDs, or MAC prefixes.
When a device matches a rule, it appears in theProfiled Devicesview.
However, matching a rule does not automatically register the device in the database unless the rule is configured to do so. If the devices appear in the view but remain " Unknown " and show " No " in the registration column, it indicates that the " Confirm " (or " Auto-register " ) action has not been triggered. In the Device Profiling Rule configuration, there is a setting called " Allow Auto-Approval " or " Confirm " . If this is not enabled, the system identifies the device but waits for an administrator to manually approve the match before changing the host status from " Unknown " to " Registered " .
This is a common " safety " configuration used during the initial deployment phase to ensure that the profiling rules are accurate before the system begins automatically granting network access based on those matches.
" If a device matches a rule but is not registered, check the rule configuration. TheConfirmoption (within the Method or Rule settings) determines if the system automatically registers the device upon a match.
IfConfirmis not enabled, the device will remain in the ' Profiled ' state with a registration status of ' No ' until an administrator manually promotes the device. " -FortiNAC-F Administration Guide: Device Profiling Rules.
NEW QUESTION # 17
Refer to the exhibits.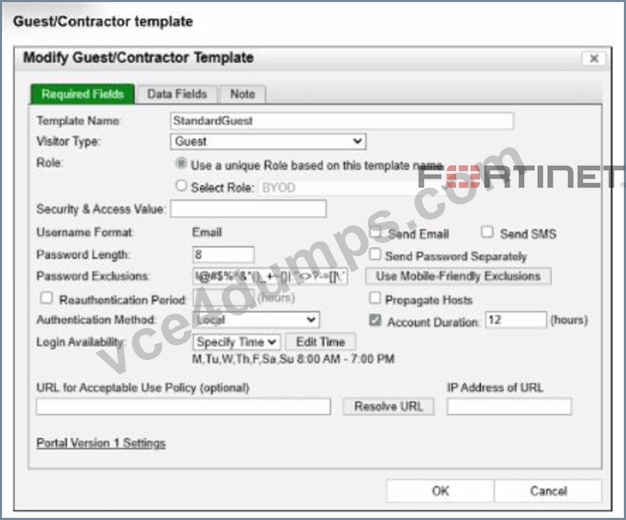
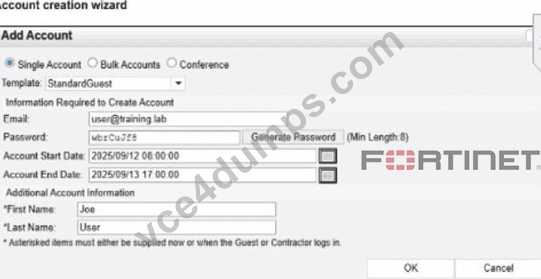
Based on the given configurations and settings, on which date and time would a guest account created at 8:00 AM on 2025/09/12 expire?
- A. 2025/09/12 at 8:00 PM
- B. 2025/09/12 at 17:00:00
- C. 2025/09/12 at 7:00 PM
- D. 2025/09/13 at 17:00:00
Answer: D
Explanation:
Questions no:22
Verified answer: D
Comprehensive and Detailed 250 to 300 words each Explanation with Exact Matched Extract from FortiNAC- F Administrator library and documentation for current versions (including F 7.2, 7.4, and 7.6) documents:
In FortiNAC-F, the expiration of a guest or contractor account is determined by the configuration settings within theAccount Creation Wizardand the associatedGuest/Contractor Template. While a template can define a default " Account Duration " (as seen in the 12-hour setting in the second exhibit), theAccount Creation Wizardallows an administrator to manually specify or override the start and end parameters for a specific user session.
According to theFortiNAC-F Administration Guideregarding guest management, theAccount End Datefield in the creation wizard is the definitive timestamp for when the account object will be disabled or deleted from the system. In the provided exhibit (Account Creation Wizard), the administrator has explicitly set theAccount Start Dateto2025/09/12 08:00:00and theAccount End Dateto2025/09/13 17:00:00.
Even though the template indicates an " Account Duration " of 12 hours, this value typically serves as a pre- populated default. When a manual date and time are entered into the wizard, those specific values take precedence for that individual account. The account will remain active and valid until5:00 PM (17:00:00)on the following day,2025/09/13. It is also important to note the " Login Availability " from the template (8:00 AM - 7:00 PM); while the accountexistsuntil the 13th at 17:00:00, the user would only be able to authenticate during the active hours defined by the login schedule on both days.
" When creating an account, the administrator can select a template to provide default settings. However, specific values such as theAccount End Datecan be modified within theAccount Creation Wizard. The date and time specified in the ' Account End Date ' field determines the absolute expiration of the account. Once this time is reached, the account is moved to an expired state and the user ' s network access is revoked. " - FortiNAC-F Administration Guide: Guest and Contractor Account Management.
NEW QUESTION # 18
An administrator wants to continually monitor endpoints for the existence of a specific registry key and the status of a required security service. Which two requirements must be in place for the administrator to use FortiNAC-F compliance monitors? (Choose two.)
- A. MDM integration
- B. Remediation admin scan
- C. Persistent agent
- D. Custom scan
Answer: C,D
Explanation:
The correct answers are B and C . FortiNAC-F must have a persistent agent on the endpoint if the goal is continual or background endpoint monitoring. The study guide states that the persistent agent is an install-and- stay resident agent and that, after deployment, it communicates back to FortiNAC-F every 15 minutes. It also performs scheduled scans in the background without normal user interaction unless the scan fails. That is the agent model required for continuous compliance monitoring, not a one-time captive portal scan.
A custom scan is also required because the administrator wants to check very specific endpoint conditions: a registry key and a security service. The FortiNAC-F study guide lists Windows custom scan types including Registry Keys and Service , which directly match the two conditions in the question.
Option A is wrong because MDM integration is used to synchronize mobile device data, retrieve MDM- known hosts, receive MDM host updates, and apply policies based on MDM attributes; it is not the required mechanism for checking Windows registry keys or Windows service status. Option D is wrong because a remediation admin scan is not what defines the compliance check itself. The compliance logic must be created as a custom scan, and continuous monitoring requires the persistent agent.
NEW QUESTION # 19
Refer to the exhibit.
A FortiNAC-F N+1 HA configuration is shown.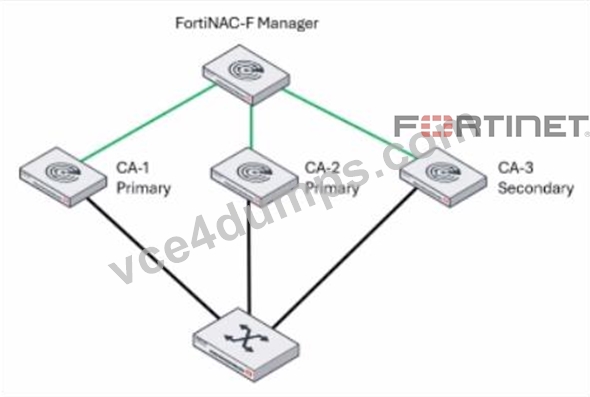
What will occur if CA-2 fails?
- A. CA-3 will continue to operate as a secondary in an N+1 HA configuration.
- B. CA-1 and CA-3 will operate as a 1+1 HA cluster with CA-3 acting as a hot standby.
- C. CA-3 will be promoted to a primary and share management responsibilities with CA-1.
- D. CA-3 will be promoted to a primary and FortiNAC-F manager will load balance between CA-1 and CA-3.
Answer: A
Explanation:
In an N+1 High Availability (HA) configuration, a single secondary Control and Application (CA) server provides backup for multiple primary CA servers. The FortiNAC-F Manager (FortiNAC-M) acts as the centralized orchestrator for this cluster, monitoring the health of all participating nodes.
According to the FortiNAC-F 7.6.0 N+1 Failover Reference Manual, when a primary CA (such as CA-2 in the exhibit) fails, the secondary CA (CA-3) is automatically promoted by the Manager to take over the specific workload and database functions of that failed primary. Crucially, the documentation specifies that even after this promotion, the system architecture maintains its N+1 logic. The secondary CA effectively "assumes the identity" of the failed primary while continuing to operate within the N+1 framework established by the Manager.
It does not merge with CA-1 to form a traditional 1+1 active/passive cluster (A), nor does it engage in load balancing (D), as FortiNAC-F HA is designed for redundancy and failover rather than active traffic distribution. Furthermore, CA-3 does not "share" management with CA-1 (C); it independently handles the tasks originally assigned to CA-2. Throughout this failover state, the Manager continues to oversee the group, and CA-3 remains the designated secondary unit currently acting in a primary capacity for the downed node until CA-2 is restored.
"In an N+1 Failover Group, the Secondary CA is designed to take over the functionality of any single failed primary component within the group. The FortiNAC Manager monitors the primaries and initiates the failover to the secondary... Once failover occurs, the secondary continues to operate as the backup unit for the failed primary while remaining part of the managed N+1 HA configuration." - FortiNAC-F 7.6.0 N+1 Failover Reference Manual: Failover Behavior Section.
NEW QUESTION # 20
An administrator has created several device profiling rules and evaluated all existing devices in the database. Some of the devices appear in the profiled devices view because they matched a rule, but they remain unknown and the registration column in the profiled devices view shows "No".
What is the most likely cause?
- A. The devices match more than one device profiling rule.
- B. The device profiling rule has registration set to manual.
- C. The confirm device profiling rule option is not enabled.
- D. The devices have persistent agents installed, and the point of connection has PA optimization enabled.
Answer: C
Explanation:
In FortiNAC-F, Device Profiling Rules are used to automatically identify and categorize devices (such as IP cameras, printers, or IoT devices) based on fingerprints like DHCP fingerprints, OIDs, or MAC prefixes. When a device matches a rule, it appears in the Profiled Devices view.
However, matching a rule does not automatically register the device in the database unless the rule is configured to do so. If the devices appear in the view but remain "Unknown" and show "No" in the registration column, it indicates that the "Confirm" (or "Auto-register") action has not been triggered. In the Device Profiling Rule configuration, there is a setting called "Allow Auto-Approval" or "Confirm". If this is not enabled, the system identifies the device but waits for an administrator to manually approve the match before changing the host status from "Unknown" to "Registered".
This is a common "safety" configuration used during the initial deployment phase to ensure that the profiling rules are accurate before the system begins automatically granting network access based on those matches.
"If a device matches a rule but is not registered, check the rule configuration. The Confirm option (within the Method or Rule settings) determines if the system automatically registers the device upon a match. If Confirm is not enabled, the device will remain in the 'Profiled' state with a registration status of 'No' until an administrator manually promotes the device." - FortiNAC-F Administration Guide: Device Profiling Rules.
NEW QUESTION # 21
During the testing of a newly modeled infrastructure switch, the administrator is not seeing hosts as they connect or move from one port to another. What would cause this issue?
- A. The default scheduled polling is disabled.
- B. Layer 3 polling is failing.
- C. MAC notification traps are misconfigured.
- D. Contact polling is not configured.
Answer: C
Explanation:
The correct answer is A . When FortiNAC-F needs near real-time Layer 2 visibility, it relies on link traps, MAC notification traps, RADIUS, or scheduled/manual Layer 2 polling. The study guide explains that MAC notification traps contain the MAC address learned or removed from the switch MAC address table and the associated port, allowing FortiNAC-F to update its database when hosts connect, disconnect, or move. It also states that MAC notification traps are the preferred method for learning and updating Layer 2 information.
If a newly modeled switch does not show hosts as they connect or move between ports, the likely problem is that MAC notification traps are not correctly configured or not reaching FortiNAC-F . Layer 3 polling failure would affect IP-to-MAC correlation, not the ability to learn which switch port a MAC address is connected to. Disabled scheduled polling could delay updates, but it would not be the best explanation when the expected behavior is immediate host detection during connection or movement testing. Contact polling only checks whether the device is reachable; it does not collect host MAC-to-port visibility.
NEW QUESTION # 22
When preparing network infrastructure devices for visibility, what are the two main advantages of using MAC notification traps on supported devices instead of link-up and link-down traps? (Choose two.)
- A. MAC notification traps include IP address information.
- B. Faster visibility updates with only a slight increase in processing.
- C. Hosts connecting to downstream non-managed hubs are immediately learned.
- D. Overhead on FortiNAC-F and the infrastructure device is reduced.
Answer: C,D
Explanation:
Comprehensive and Detailed Explanation From Exact Extract of FortiNAC-F 7.6 Administrator Guide or Knowledge:
Exact Extract:
The FortiNAC-F study guide states that MAC notification traps are preferred because FortiNAC-F does not need to connect back to the infrastructure device every time a link-up or link-down trap is received. The required MAC and port information is already included in the MAC notification trap, which makes database updates faster and uses fewer resources. It also states that hosts and devices connected through hubs or IP phones are seen immediately, even when the downstream device cannot generate link-up or link-down traps.
Technical Deep Dive:
The correct answers are B and C . With link-up/link-down traps, the trap only tells FortiNAC-F that an interface changed state. FortiNAC-F then has to perform an L2 poll against the switch forwarding table to discover which MAC address appeared or disappeared. That means extra SNMP/CLI activity, more delay, and more processing on both FortiNAC-F and the switch. The guide confirms that link traps trigger FortiNAC- F to perform a Layer 2 poll, while MAC notification traps directly contain the learned or removed MAC address and associated port.
Option A is wrong because MAC notification traps are Layer 2 visibility events. They identify MAC address and port , not IP address. IP-to-MAC correlation comes from Layer 3 polling or DHCP fingerprinting, not MAC notification traps. Option D is badly worded and should not be selected: MAC notification traps do provide faster updates, but the processing overhead is reduced, not slightly increased.
Operationally, on supported switches you enable SNMP traps for MAC address-table changes and point the trap destination to FortiNAC-F. On Cisco-style infrastructure, this is usually done with commands such as snmp-server host < FortiNAC-IP > version 2c < community > plus MAC notification trap configuration. Do not enable MAC notification traps on uplinks, because uplinks learn many downstream MAC addresses and would create misleading endpoint-location data.
NEW QUESTION # 23
When working with a FortiNAC-F Manager and cluster management, what will occur when a cluster manager recovers from a non-responsive state?
- A. It will be removed from the cluster and placed in a standalone group.
- B. It automatically returns to the manager state.
- C. It rejoins the cluster as a worker node.
- D. It will perform a health check and be demoted to standby.
Answer: C
Explanation:
The correct answer is C . In FortiNAC-F Manager clustering, the active cluster management role is the leader role, and other cluster members operate as worker nodes. Fortinet's FortiNAC-F 7.6 Manager Cluster Guide states that when a worker is promoted to leader during automatic transition, the original leader becomes a worker node when it comes back online. It also explains that a cluster has one leader and can have multiple workers, with leader/worker roles used for cluster management and heartbeat exchange.
So, if the cluster manager becomes non-responsive and another node takes over leadership, the recovered manager does not automatically reclaim the leader role. It rejoins as a worker node. Option A is wrong because recovery does not automatically remove it into a standalone group. Option B is wrong because automatic return to the previous manager/leader state would create instability and possible split-brain behavior. Option D is wrong because "standby" is not the role described for FortiNAC-F Manager clustering in this context; the documented cluster roles are leader and worker.
NEW QUESTION # 24
When creating a device profiling rule, what are two advantages of registering the device in the host view?
(Choose two.)
- A. The devices will have connection logs.
- B. The devices can be polled for connection status.
- C. The devices can be associated with a user.
- D. The devices can be managed as a generic SNMP device.
Answer: A,C
Explanation:
In FortiNAC-F, theDevice Profileris a rule-based engine that evaluates unknown " rogue " devices and classifies them based on fingerprints and behavior. When a profiling rule matches a device, the administrator can configure the rule to automatically register that device. The registration process can place the device record in two primary locations: theTopology View(as a device) or theHost View(as a registered host).
According to theFortiNAC-F Administration Guide, registering a device in theHost Viewprovides significant advantages for identity management and historical tracking. First, the devices can beassociated with a user (C). In the FortiNAC database architecture, the Host View is the primary repository for endpoint identity; placing a profiled device here allows the system to link that hardware (MAC address) to a specific user account, whether that user is an employee, guest, or a system-level " owner " . This association is essential for Role-Based Access Control (RBAC) and for tracking accountability across the network fabric.
Second, devices registered in the Host View will haveconnection logs (B). FortiNAC-F maintains a detailed operational history for all host records, including every instance of the device connecting to or disconnecting from a port, its IP address assignments, and the specific policies applied during each session. These logs are invaluable for troubleshooting connectivity issues and for security forensic audits, as they provide a clear timeline of the device ' s lifecycle on the network. In contrast, devices managed only in the Topology View are typically treated as infrastructure components where the focus is on device availability rather than individual session history.
" Devices that are registered and associated with a user are placed in theHost Viewand removed from the Profiled Devices window... Placing a device in the Host View allows for the tracking ofconnection historyand the association of the device with a specificidentity or user recordwithin the FortiNAC database. " - FortiNAC-F Administration Guide: Device Profiler How it Works.
NEW QUESTION # 25
Refer to the exhibit.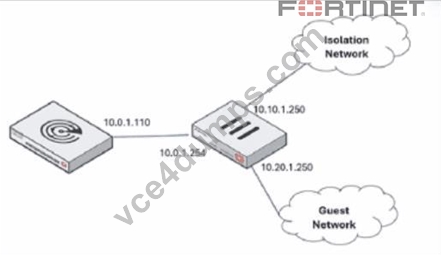
An administrator is configuring FortiNAC-F (or the onboarding of guest users. Which IP address would be used for the gateway defined in the DHCP scope?
- A. 10.20.1.250
- B. 10.0.1.254
- C. 10.0.1.110
- D. 10.10.1.250
Answer: A
Explanation:
The correct answer is D . The question is about guest onboarding , and the exhibit shows the Guest Network using gateway 10.20.1.250 . In a Layer 3 captive network design, FortiNAC-F provides DHCP and DNS services to isolated or captive-network hosts, but the DHCP scope must still give the endpoint the correct default gateway for the network where that endpoint is placed. The study guide specifically warns that, when configuring Layer 3 captive network scopes, the administrator must think from the isolated host's perspective for the IP pool and gateway configuration . It also states that each captive network interface configuration includes an IP address, subnet mask, default gateway, and one or more DHCP scopes.
Option A , 10.0.1.254 , is the infrastructure gateway on the FortiNAC-F service/production-side segment, not the guest network gateway. Option B , 10.0.1.110 , is the FortiNAC-F interface address shown in the diagram, not the default gateway for guest clients. Option C , 10.10.1.250 , is the gateway for the Isolation Network , not the Guest Network . Since the administrator is configuring guest onboarding, the DHCP scope for guest users must hand out 10.20.1.250 as the gateway.
NEW QUESTION # 26
An administrator wants to build a security rule that will quarantine contractors who attempt to access specific websites.
In addition to a user host profile, which Iwo components must the administrator configure to create the security rule? (Choose two.)
- A. Security String
- B. Action
- C. Trigger
- D. Endpoint compliance policy
- E. Methods
Answer: B,C
Explanation:
In FortiNAC-F, the Security Incidents engine is used to automate responses to security threats reported by external devices. When an administrator wants to enforce a policy, such as quarantining contractors who access restricted websites, they must create a Security Rule. A Security Rule acts as the "if-then" logic that correlates incoming security data with the internal host database.
The documentation specifies that a Security Rule consists of three primary configurable components:
User/Host Profile: This identifies who or what the rule applies to (in this case, "Contractors").
Trigger: This is the event that initiates the rule evaluation. In this scenario, the Trigger would be configured to match specific syslog messages or NetFlow data indicating access to prohibited websites. Triggers use filters to match vendor-specific data, such as a "Web Filter" event from a FortiGate.
Action: This defines what happens when the Trigger and User/Host Profile are matched. For this scenario, the administrator would select a "Quarantine" action, which instructs FortiNAC-F to move the endpoint to a restricted VLAN or apply a restrictive ACL.
While "Methods" (A) relate to authentication and "Security Strings" (E) are used for specific SNMP or CLI matching, they are not the structural components of a Security Rule in the Security Incidents menu.
"Security Rules are used to perform a specific action based on certain criteria... To configure a Security Rule, navigate to Logs > Security Incidents > Rules. Each rule requires a Trigger to define the event criteria, an Action to define the automated response (such as Quarantine), and a User/Host Profile to limit the rule to specific groups." - FortiNAC-F Administration Guide: Security Rules and Incident Management.
NEW QUESTION # 27
In which three ways would deploying a FortiNAC-F Manager into a large environment consisting of several FortiNAC-F CAs simplify management? (Choose three.)
- A. Global version control
- B. Global authentication security policies
- C. Pooled licenses
- D. Global visibility
- E. Global infrastructure device inventory
Answer: A,C,D
Explanation:
TheFortiNAC-F Manager (FortiNAC-M)is designed as a centralized management platform for large-scale distributed environments where multiple FortiNAC-F Control and Application (CA) appliances are deployed across different sites. According to theFortiNAC-F Manager Administration Guide, the deployment of a Manager simplifies administrative overhead in three specific ways:
First, it providesGlobal Version Control (B). The Manager serves as a central repository for firmware and software updates, allowing administrators to push specific versions to all managed CAs simultaneously, ensuring consistency across the entire fabric. Second, it enablesPooled Licenses (D). Instead of purchasing and managing individual licenses for every CA, licenses are centralized on the Manager. The Manager then distributes these licenses to the CAs as needed based on their host counts. This " floating " license model optimizes cost and prevents individual sites from running out of capacity while others have excess. Third, it offersGlobal Visibility (E). The Manager aggregates host and device data from every managed CA into a single console. This " single pane of glass " allows an administrator to search for a specific MAC address or user across the entire global organization without logging into individual servers.
While the Manager can assist with configuration templates, authentication security policies (C) and infrastructure modeling (A) are still predominantly managed at the local CA level to ensure site-specific logic and performance.
" The FortiNAC Manager provides a central management console for multiple FortiNAC-F servers (CAs).
Key benefits include: *License Management: Licenses are pooled on the Manager and allocated to managed CAs as needed. *Software Management: Firmware updates can be centrally managed and pushed to all CAs from the Manager. *Centralized Monitoring: Provides a global view of all hosts, adapters, and events across the entire managed environment. " -FortiNAC-F Manager Administration Guide: Overview and Benefits.
NEW QUESTION # 28
When FortiNAC-F is managing VPN clients connecting through FortiGate, why must the clients run a FortiNAC-F agent?
- A. To validate the endpoint policy compliance
- B. To collect user authentication details
- C. To collect the client IP address and MAC address
- D. To transparently update The client IP address upon successful authentication
Answer: C
Explanation:
When FortiNAC-F manages VPN clients through a FortiGate, the agent plays a fundamental role in device identification that standard network protocols cannot provide on their own. In a standard VPN connection, the FortiGate establishes a Layer 3 tunnel and assigns a virtual IP address to the client. While the FortiGate sends a syslog message to FortiNAC-F containing the username and this assigned IP address, it typically does not provide the hardware (MAC) address of the remote endpoint ' s physical or virtual adapter.
FortiNAC-F relies on theMAC addressas the primary unique identifier for all host records in its database.
Without the MAC address, FortiNAC-F cannot correlate the incoming VPN session with an existing host record to apply specific policies or track the device ' s history. By running either a Persistent or Dissolvable Agent, the endpoint retrieves its own MAC address and communicates it directly to the FortiNAC-F service interface. This allows the " IP to MAC " mapping to occur. Once FortiNAC-F has both the IP and the MAC, it can successfully identify the device, verify its status, and send the appropriateFSSO tagsor group information back to the FortiGate to lift network restrictions.
Furthermore, while the agent can also perform compliance checks (Option D), the architectural requirement for the agent in a managed VPN environment is primarily driven by the need for session data correlation- specifically the collection of the IP and MAC address pairing.
" Session Data Components: * User ID (collected via RADIUS, syslog and API from the FortiGate). * Remote IP address for the remote user connection (collected via syslog and API from the FortiGate and from the FortiNAC agent). *Device IP and MAC address (collected via FortiNAC agent).... The Agent is used to provide the MAC address of the connecting VPN user (IP to MAC). " -FortiNAC-F FortiGate VPN Integration Guide: How it Works Section.
NEW QUESTION # 29
An organization wants to add a FortiNAC-F Manager to simplify their large FortiNAC-F deployment.
Which two policy types can be managed globally? (Choose two.)
- A. Supplicant EasyConnect
- B. Endpoint Compliance
- C. Authentication
- D. Network Access
Answer: B,D
Explanation:
The FortiNAC-F Manager is designed to centralize the management of multiple Control and Application (CA) appliances, ensuring consistent security posture across a distributed enterprise. To achieve this, the Manager allows administrators to define and distribute specific types of policies globally rather than configuring them on each individual CA.
According to the FortiNAC Manager Guide, the two primary policy types that are managed globally are:
Network Access Policies (D): These policies define the "If-Then" logic for network entry. By managing these at the global level, an administrator can ensure that a "Contractor" receives the same restricted access regardless of which branch office or campus they connect to.
Endpoint Compliance Policies (B): Global management of compliance policies-which consist of scans and configurations-allows for a unified security baseline. For example, a global policy can mandate that all Windows devices across the entire organization must have a specific antivirus version installed and active before gaining access to the production network.
While the Manager provides visibility into authentication events and can synchronize directory data, the specific Authentication (A) configurations (like local RADIUS secrets or specific LDAP server links) are often localized to the CA to account for site-specific infrastructure. Supplicant EasyConnect (C) is a feature set for onboarding, but the structural "Global Policy" engine focuses primarily on the Access and Compliance frameworks.
"The FortiNAC Manager enables Global Policy Management, allowing for the creation and distribution of policies across all managed CA appliances. This includes Network Access Policies, which control VLAN and ACL assignment, and Endpoint Compliance Policies, which define the security requirements for hosts. Centralizing these policies ensures that security standards are enforced uniformly across the global network fabric." - FortiNAC Manager Administration Guide: Global Policy Management Overview.
NEW QUESTION # 30
During an evaluation of state-based enforcement, an administrator discovers that ports that should not be under enforcement have been added to enforcement groups.
In which view would the administrator be able to identify who added the ports to the groups?
(Selected)
- A. The Port Changes view
- B. The Admin Auditing view
- C. The Event Management view
- D. The Security Events view
Answer: B
Explanation:
In FortiNAC-F, accountability and forensic tracking of configuration changes are managed through theAdmin Auditingfunctionality. When an administrator performs an action that modifies the system state-such as creating a policy, changing a device ' s status, or adding a switch port to anEnforcement Group-the system generates an audit record. This record is essential for troubleshooting scenarios where unauthorized or accidental configuration changes have occurred, leading to unintended network behavior.
TheAdmin Auditingview (found underLogs > Admin Auditing) provides a comprehensive log of the " Who, What, and When " for every administrative session. Each entry includes the username of the administrator, the source IP address from which they accessed the FortiNAC-F console, a precise timestamp, and a detailed description of the modification. In the scenario described, where ports have been incorrectly added to enforcement groups, the Admin Auditing view allows a supervisor to filter by the specific " Port " or " Group
" object to identify exactly which administrator executed the command.
In contrast, theEvent Managementview (B) is designed to monitor system and network events, such as RADIUS authentications, host connections, and SNMP trap arrivals. While it tracks system activity, it does not typically log the manual configuration changes performed by admins. ThePort Changesview (C) tracks the operational history of a port (such as VLAN assignment changes and host movements) but does not attribute the administrative assignment of the port to a group. Finally, theSecurity Eventsview (D) is dedicated to alerts triggered by security rules and external threat feeds.
" Admin Auditing displays a record of all modifications made to the FortiNAC-F system by an administrator.
This view includes the administrator ' s name, the date and time of the change, and a description of the action taken. It is the primary resource for determining which administrative user performed a specific configuration change, such as modifying port group memberships or altering policy settings. " -FortiNAC-F Administration Guide: Logging and Auditing Section.
NEW QUESTION # 31
When configuring FortiNAC-F to manage FortiGate VPN users, an endpoint compliance policy must be created for the integration.
Why is the endpoint compliance policy necessary for this type of integration?
- A. To designate the required agent type
- B. To confirm the installed endpoint certificate
- C. To validate the VPN client being used
- D. To validate the VPN user credentials
Answer: A
Explanation:
The integration of FortiNAC-F with FortiGate VPN requires a specific policy workflow to bridge the gap between initial user authentication and full network access. When a user connects to the VPN, the FortiGate typically provides the User ID and IP address, but FortiNAC-F requires a MAC address to uniquely identify and manage the endpoint's record.
According to the FortiGate VPN Integration Guide, the Endpoint Compliance Policy is a mandatory component of this setup because it is used to designate the required agent type. Because a VPN connection is Layer 3, FortiNAC cannot "see" the MAC address through traditional SNMP or L2 polling. The compliance policy instructs the system to present a Captive Portal to the remote user, requiring them to download and run either the Persistent or Dissolvable Agent. The agent then reports the device's MAC address back to FortiNAC, allowing the system to correlate the VPN session with a host record.
Once the agent is running and the MAC is known, FortiNAC-F can evaluate the device's security posture (if scanning is configured) and send the necessary FSSO tags back to the FortiGate to lift the initial network restrictions. Without the compliance policy to enforce the agent requirement, the connection would remain in an isolated "IP-only" state with no unique hardware identity.
"The Endpoint Compliance Policy is necessary to control the agent requirement for VPN users. Create a default VPN Endpoint Compliance Policy to distribute an agent via captive portal for isolated machines. This policy allows the administrator to designate the required agent type (Persistent or Dissolvable) that will be used to collect the hardware (MAC) address and perform health scans on the remote endpoint." - FortiNAC FortiGate VPN Integration Guide: Default Endpoint Compliance Policy (Optional) Section.
NEW QUESTION # 32
A user was attempting to register their host through the registration captive portal. After successfully registering, the host remained in the registration VLAN. Which two conditions would cause this behavior? (Choose two.)
- A. The port default VLAN is the same as the Registration VLAN.
- B. There is no agent installed on the host.
- C. The wrong agent s installed.
- D. There is another unregistered host on the same port
Answer: A,D
Explanation:
The process of moving a host from a Registration VLAN to a Production VLAN (Access VLAN) is a fundamental part of the FortiNAC-F "VLAN steering" workflow. When a host successfully registers via the captive portal, FortiNAC-F evaluates its Network Access Policies to determine the correct VLAN. If the host remains stuck in the Registration VLAN despite a successful registration, it is typically due to port-level restrictions or the presence of other unregistered devices.
The two most common reasons for this behavior as per the documentation are:
The port default VLAN is the same as the Registration VLAN: If the "Default VLAN" field in the switch port's model configuration is set to the same ID as the Registration VLAN, the port will not change state because FortiNAC-F believes it is already in its "normal" or "forced" state.
There is another unregistered host on the same port: FortiNAC-F maintains the security posture of the physical port. If multiple hosts are connected to a single port (e.g., via a hub or unmanaged switch) and at least one host remains "Rogue" (unregistered), FortiNAC-F will generally keep the entire port in the isolation/registration VLAN to prevent the unregistered host from gaining unauthorized access to the production network.
Issues with agents (A, B) typically prevent a host from completing compliance or registration but do not usually result in a "stuck" status after registration has already been marked as successful in the system.
"If a port is identified as having Multiple Hosts, and those hosts require different levels of access, FortiNAC remains in the most restrictive state (Registration or Isolation) until all hosts on that port are authorized... Additionally, verify the Default VLAN setting for the port; if the Default VLAN and Registration VLAN match, the system will not trigger a VLAN change upon registration." - FortiNAC-F Administration Guide: Troubleshooting Host Management.
NEW QUESTION # 33
......
Fortinet NSE5_FNC_AD_7.6 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
| Topic 4 |
|
Updated NSE5_FNC_AD_7.6 Dumps Questions For Fortinet Exam: https://passguide.vce4dumps.com/NSE5_FNC_AD_7.6-latest-dumps.html