


View All 1Z0-1109-25 Actual Exam Questions Answers and Explanations for Free Mar-2026
The Most In-Demand Oracle 1Z0-1109-25 Pass Guaranteed Quiz
Oracle 1Z0-1109-25 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
NEW QUESTION # 13
The Kubernetes Master node serves as the central control plane for managing the cluster's resources and orchestrating workload deployment.
What are the primary responsibilities of the Kubernetes Master node?
- A. The Master node oversees the scheduling and allocation of cluster resources, ensuring optimal utilization across nodes.
- B. The Master node serves as a repository for storing container images, facilitating rapid deployment and scaling of applications.
- C. The Master node monitors network traffic within the cluster, ensuring secure communication and efficient data transfer between nodes.
- D. The Master node is primarily tasked with executing application workloads and ensuring their availability within the cluster.
Answer: A
Explanation:
The Kubernetes Master node is the central control plane responsible for managing the cluster's resources and orchestrating workload deployment. Its primary responsibilities include:
Scheduling: Deciding which workloads (pods) should run on which worker nodes, based on resource availability and scheduling constraints.
Resource Allocation: Allocating resources to workloads to ensure optimal utilization across nodes.
Cluster Management: Maintaining the desired state of applications, managing cluster events, and ensuring that all the components of the cluster are functioning properly.
NEW QUESTION # 14
Your team is working on a project to deploy a microservices-based application on a cloud platform using Terraform. Each microservice has specific configurations and dependencies, and you want to ensure modularity, reusability, and consistency across deployments.
Which Terraform feature would you use to achieve these objectives efficiently?
- A. Terraform Workspaces
- B. Terraform Variables
- C. Terraform Modules
- D. Terraform Providers
Answer: C
Explanation:
Terraform Modules are used to organize and group related configuration resources into reusable components. By using modules, you can achieve modularity, reusability, and consistency across different deployments, making it easier to manage complex infrastructure setups.
For a microservices-based application, where each microservice has specific configurations and dependencies, modules allow you to define the infrastructure for each microservice in a modular way. This helps to maintain clean, reusable code and ensures consistency across deployments.
NEW QUESTION # 15
How do OCI DevOps Deployment Pipelines reduce risk and complexity of production applications?
- A. By working with existing Git repositories and CI systems
- B. By reducing change-driven errors introduced by manual deployments
- C. By scaling builds with service-managed build runners
- D. By eliminating downtime of production applications
Answer: B
Explanation:
OCI DevOps Deployment Pipelines automate the process of deploying applications to production environments. By using automated, repeatable deployment processes, they help reduce the risk of change-driven errors, which are often introduced during manual deployments. This automation reduces human errors and ensures consistency across environments, thus minimizing complexity and risk in production.
NEW QUESTION # 16
As an engineer building and deploying applications using an OCI DevOps project, which two capabilities can help ensure the security and reliability of the code in the build and deployment pipelines? (Choose two.)
- A. Using JIRA to track user stories and bug fixes in the development process
- B. Using third-party tools like Sonatype, SonarQube, or OverOps to analyze code for security defects or bugs in code quality
- C. Using third-party tools like Ansible, Terraform, or OverOps to analyze code for security defects or bugs in code quality
- D. Using version control tools like Git or SVN to track and manage changes in the codebase
- E. Using Application Dependency Management (ADM) to identify security weaknesses in software applications by checking their dependencies
Answer: B,E
NEW QUESTION # 17
Observability helps understand system behavior, but it has limitations.
Which of the following tasks cannot be accomplished solely through observability?
- A. Identifying resource consumption
- B. Optimizing resource utilization
- C. Automating software deployments
- D. Identifying infrastructure bottlenecks
Answer: C
Explanation:
Observability refers to the ability to understand a system's internal state by observing its outputs. It involves metrics, logs, and tracing to provide insights into the system's behavior, which helps in monitoring and identifying issues.
NEW QUESTION # 18
You're using Oracle Cloud Infrastructure (OCI) DevOps to deploy your application on an Oracle Container Engine for Kubernetes (OKE) environment. You push your code to the OCI Code Repository, add all the required stage and configure the build and deployment pipeline. When you run the build, you see "unable to clone the repository" error.
What could the configuration error be?
- A. The OKE cluster is not configured to allow external access to the code repository.
- B. The Docker image used in the pipeline is incompatible with the OKE environment.
- C. Dynamic Groups and OCI IAM policies to access the code repository are missing.
- D. CA bundle for Transport Layer Security (TLS) verification to download the build source during the build run is missing.
Answer: C
Explanation:
The error "unable to clone the repository" typically indicates that there is an authentication or authorization issue preventing access to the OCI Code Repository. In OCI DevOps, the build pipeline must have the appropriate permissions to access the code repository.
To allow the build pipeline to clone the repository, you need to set up Dynamic Groups and OCI IAM policies that provide the necessary permissions for the build runner to access the code repository.
NEW QUESTION # 19
A fully qualified path to a particular image in an OCIR repository is given as iad.ocir.io/ansh81vru1zp/project01/acme-web-app:version2.0.test.
Identify the two options with correct terms and their associated values. (Choose two.)
- A. ansh81vru1zp represents <tenancy-namespace>
- B. iad.ocir.io/ansh81vru1zp represents <region-key>
- C. version2.0.test represents <tenancy-namespace>
- D. ansh81vru1zp/project01/acme-web-app:version2.0.test represents <repo-name>
- E. iad represents <region-key>
Answer: A,E
Explanation:
ansh81vru1zp is the <tenancy-namespace>. In Oracle Cloud Infrastructure Registry (OCIR), the tenancy namespace uniquely identifies the tenancy and is used as part of the image path.
iad is the <region-key>. The region key is the shorthand identifier for the OCI region (iad represents Ashburn region), and it is used in the fully qualified path for images stored in the Oracle Cloud Infrastructure Registry (OCIR).
NEW QUESTION # 20
Which two are prerequisites for creating a secret in Oracle Cloud Infrastructure Vault service? (Choose two.)
- A. You must have an auth token to encrypt the secret.
- B. The user must create a compute instance to run the secret service.
- C. You must have the required permissions to create and manage secrets in the Vault service.
- D. You must first create a hash digest of the secret value.
- E. You must have a Vault managed key to encrypt the secret.
Answer: C,E
Explanation:
You need the required permissions (such as policies allowing secret management) to create and manage secrets in Oracle Cloud Infrastructure (OCI) Vault service. These permissions are essential for performing operations such as creating, reading, and managing secrets.
Vault managed key is required to encrypt the secret before it is stored in the OCI Vault. The managed key acts as the encryption key for securing the secret, ensuring its confidentiality.
NEW QUESTION # 21
A software development team is working on a prototype using Node.js and MongoDB as their programming language and database, respectively. They need to develop and test isolated web applications or RESTful APIs. They are looking for a simple, quick, and secure way to run containers without managing any servers.
Which OCI service is best suited for this use case?
- A. Compute Instances
- B. OCI Functions
- C. Container Instances
- D. OCI DevOps Project
Answer: C
Explanation:
OCI Container Instances provide a serverless way to run containers in Oracle Cloud Infrastructure (OCI). They allow you to run containers without having to manage any underlying servers or clusters. This is ideal for development teams that need a simple, quick, and secure way to develop and test isolated web applications or RESTful APIs.
NEW QUESTION # 22
How can system administrators ensure that only signed images from Oracle Cloud Infrastructure Registry are deployed to a Container Engine for Kubernetes cluster?
- A. By disabling access to the Container Engine for Kubernetes cluster
- B. By manually inspecting each image before deployment
- C. By encrypting the images using a custom encryption algorithm
- D. By configuring an image verification policy for the cluster
Answer: D
Explanation:
Image verification policies are used to ensure that only trusted and signed images are deployed to an Oracle Kubernetes Engine (OKE) cluster. By configuring such policies, administrators can enforce that images must be signed and come from trusted sources, such as the Oracle Cloud Infrastructure Registry.
NEW QUESTION # 23
An operations team wants to leverage the advanced features of Container Engine for Kubernetes (OKE) and requires granular control over cluster add-ons, workload identity, and improved worker node management. They also prioritize strong security measures and require a financially-backed service level agreement (SLA) for Kubernetes API server uptime.
Which type of cluster should they choose to meet their requirements?
- A. Federated clusters
- B. Specialized clusters
- C. Enhanced clusters
- D. Virtual clusters
Answer: C
Explanation:
Enhanced clusters in Oracle Container Engine for Kubernetes (OKE) provide advanced features such as granular control over cluster add-ons, workload identity, and improved worker node management. They also offer strong security measures and come with a financially-backed service level agreement (SLA) for Kubernetes API server uptime, ensuring higher reliability and support for production workloads.
NEW QUESTION # 24
Your team is responsible for deploying a new version of an application that is being used by your company's finance department. The application is critical to the department's operations, and any downtime could have serious consequences.
What is the recommended approach in OCI for creating environments for this scenario?
- A. Use a single Kubernetes cluster with two node pools, one for the blue-green environment and one for the canary environment.
- B. Configure two OKE clusters, selecting the blue-green traffic shift strategy using a load balancer.
- C. Deploy the application to two separate OCI tenancies to ensure complete isolation between environments.
- D. Use a single OCI region and create two separate Virtual Cloud Networks (VCNs), one for the blue environment and one for the green environment.
Answer: A
Explanation:
For critical applications, such as the one used by the finance department, a blue-green deployment strategy is recommended to ensure minimal or zero downtime during upgrades. The blue-green strategy involves running two separate environments: blue (current version) and green (new version).
NEW QUESTION # 25
As a DevOps Engineer, you are tasked with explaining the key concepts of Terraform to a new team member. You want to ensure they understand the fundamental concepts of Terraform.
Which of the following best describes the purpose of Terraform variables?
- A. Terraform variables are used to output the final state of the infrastructure after deployment.
- B. Terraform variables are used to define input values for Terraform configurations, allowing for customization and reuse of infrastructure code.
- C. Terraform variables are used to manage the life cycle of Terraform resources.
- D. Terraform variables are used to define the structure and organization of Terraform configuration files.
Answer: B
Explanation:
Terraform variables are used to define input values for Terraform configurations. They allow users to customize infrastructure deployments by providing different values without modifying the configuration files themselves. Variables help in creating reusable infrastructure code, making it easy to maintain and adjust the infrastructure setup according to different environments or needs.
NEW QUESTION # 26
Which statement is false about OCI Resource Manager (RM)?
- A. RM can mirror repositories from GitHub and GitLab.
- B. Resources provisioned through RM cannot be destroyed from outside of RM.
- C. RM can render custom "Application Information" pages for stacks.
- D. RM can generate Terraform based on the resources in a compartment.
Answer: B
Explanation:
Resources provisioned through OCI Resource Manager (RM) can still be modified or destroyed from outside of RM, such as using the OCI Console, CLI, or other APIs. RM manages the lifecycle of resources created by its Terraform configurations, but it does not prevent other tools or methods from modifying or deleting those resources.
NEW QUESTION # 27
As a DevOps engineer working on containerizing a microservices-based application to be hosted on OCI Cloud platforms, which step can help ensure that the container images have not been modified after being pushed to Oracle Cloud Infrastructure Registry (OCIR)?
- A. Deploying a manifest to the Kubernetes cluster that references the container image and its unique hash
- B. Signing the image using the Container Registry CLI and creating an image signature that associates the image with the master encryption key and key version in the Vault service
- C. Scanning the image upon ingestion and comparing the image size for changes
- D. Enabling scanning of container images stored in OCI Registry
Answer: B
Explanation:
To ensure that container images have not been modified after being pushed to the Oracle Cloud Infrastructure Registry (OCIR), you should sign the image. This involves using the Container Registry CLI to create a digital signature for the image, which associates the image with a master encryption key and key version stored in the OCI Vault service. This signature can then be verified at the time of deployment, ensuring that the image has not been tampered with since it was signed.
NEW QUESTION # 28
Which is NOT a valid log category for the Oracle Cloud Infrastructure Logging service?
- A. Custom Logs
- B. Audit Logs
- C. Execution Logs
- D. Service Logs
Answer: C
Explanation:
The Oracle Cloud Infrastructure Logging service has several log categories that users can utilize:
Custom Logs: Users can create their own logs to collect application-specific data.
Audit Logs: These logs contain audit records that provide information about activities performed on resources, generated by OCI Audit service.
Service Logs: These are logs generated by OCI services, providing information about the functioning and performance of the services.
Execution Logs is not a valid log category in OCI Logging. There are no "execution logs" as a defined category for the Logging service.
NEW QUESTION # 29
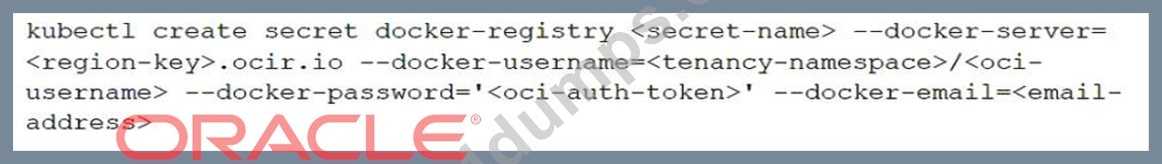
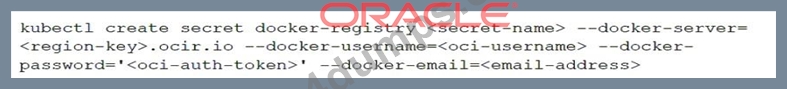
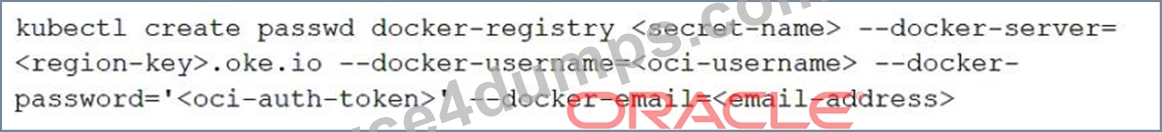
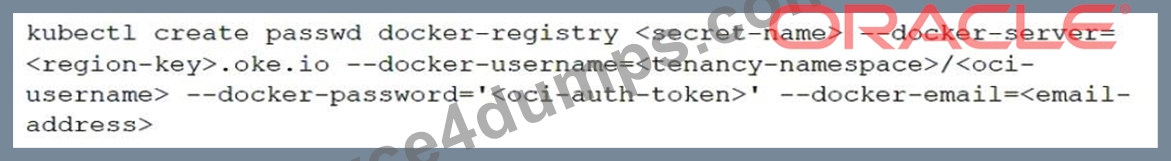
Which command creates the docker registry secret required in the application manifests for OKE to pull images from Oracle Cloud Infrastructure Registry?
- A.
- B.
- C.
- D.
Answer: A
Explanation:
To create a Docker registry secret to pull images from the Oracle Cloud Infrastructure Registry (OCIR), you need to specify the correct parameters such as the region key, namespace, OCI username, and OCI authentication token.
Chosen command is correct because:
The kubectl create secret docker-registry command creates a Docker registry secret.
The --docker-server=<region-key>.ocir.io specifies the correct endpoint for OCIR.
The --docker-username=<tenancy-namespace>/<oci-username> provides both the tenancy namespace and the OCI username, which is the required format for authentication with OCIR.
The --docker-password='<oci-auth-token>' specifies the OCI auth token, which acts as a password for authentication.
The --docker-email=<email-address> is also included.
The other commands have errors, such as missing tenancy namespace or using incorrect flags (passwd instead of secret).
NEW QUESTION # 30
A DevOps team is deploying a new version of their application to their production environment using the Canary deployment strategy in the OCI DevOps service. They want to ensure that the production environment is not affected by any potential issues caused by the new version.
Which statement is true in regards to the Canary deployment strategy?
- A. The Shift Traffic stage in the Canary deployment strategy shifts the entire 100% of the production traffic to the Canary environment.
- B. The Invoke Function stage is an optional stage that can be used to validate the new version before moving to the production environment.
- C. The Canary deployment strategy only supports pipeline redeployment for OKE and not for instance group deployments.
- D. The Production stage in the Canary deployment strategy deploys the new version to the production environment without any manual approval.
Answer: B
Explanation:
In a Canary deployment strategy, a new version of an application is rolled out to a small subset of the production environment (the canary) first, while the majority of the production environment still runs the current stable version. This approach helps to detect potential issues before the new version is fully deployed.
The Invoke Function stage can be used as an optional step in the deployment pipeline to run additional validation (e.g., automated tests or other checks) on the new version before gradually shifting more traffic to it or moving to full production deployment.
NEW QUESTION # 31
What is the correct approach to upgrade an Oracle Container Engine for Kubernetes (OKE) Cluster to a newer version of Kubernetes?
- A. Upgrade the node pools one at a time, then once all node pools are upgraded, upgrade the control plane.
- B. Initiate the automated upgrade process using the OCI Console, CLI, or API.
- C. Upgrade the control plane, then upgrade the node pools.
- D. Initiate the control plane and node pool upgrades simultaneously.
Answer: C
Explanation:
The correct approach to upgrade an Oracle Container Engine for Kubernetes (OKE) cluster involves first upgrading the Kubernetes control plane, followed by upgrading the node pools. The control plane must be upgraded first to ensure compatibility with newer versions of Kubernetes, as node pools rely on the control plane for orchestration and management.
After upgrading the control plane, each node pool is upgraded to match the new Kubernetes version. This phased approach ensures the cluster remains in a stable state during the upgrade.
NEW QUESTION # 32
......
1Z0-1109-25 Free Certification Exam Material with 52 Q&As : https://passguide.vce4dumps.com/1Z0-1109-25-latest-dumps.html