


Updated Nov-2023 Premium Essentials Exam Engine pdf - Download Free Updated 75 Questions
Authentic Essentials Dumps With 100% Passing Rate Practice Tests Dumps
NEW QUESTION # 16
Match each type of NAT with the correct description:
Conserves IP addresses and hides the internal topology of your network. (Choose one)
- A. Dynamic NAT
- B. 1-to1 NAT
- C. NAT Loopback
Answer: A
Explanation:
Explanation/Reference:
Dynamic NAT is also known as IP masquerading. With dynamic NAT many computers can connect to the Internet from one public IP address. Dynamic NAT gives more security for internal hosts that use the Internet, because it hides the IP addresses of hosts on your network.
Reference: http://www.watchguard.com/help/docs/wsm/xtm_11/en-US/index.html#en-US/nat/ nat_dynamic_use_c.html%3FTocPath%3DNetwork%2520Address%2520Translation%2520(NAT)%7CAbout%
2520Dynamic%2520NAT%7C_____0
NEW QUESTION # 17
Which of these threats can the Firebox prevent with the default packet handling settings? (Select four.)
- A. Viruses in email messages
- B. Malware in downloaded files
- C. Access to inappropriate websites
- D. IP spoofing
- E. Port scans
- F. Flood attacks
- G. Denial of service attacks
Answer: D,E,F,G
Explanation:
Explanation/Reference:
B: The default configuration of the XTM device is to block DDoS attacks.
C: In a flood attack, attackers send a very high volume of traffic to a system so it cannot examine and allow permitted network traffic. For example, an ICMP flood attack occurs when a system receives too many ICMP ping commands and must use all of its resources to send reply commands. The XTM device can protect against these types of flood attacks: IPSec, IKE, ICMP. SYN, and UDP.
E: When the Block Port Space Probes (port scans) and Block Address Space Probes check boxes are selected, all incoming traffic on all interfaces is examined by the XTM device.
CG: Default packet handling can reject a packet that could be a security risk, including packets that could be part of a spoofing attack or SYN flood attack Reference: http://www.watchguard.com/help/docs/wsm/xtm_11/en-US/index.html#en-US/intrusionprevention/ default_pkt_handling_opt_about_c.html%3FTocPath%3DDefault%2520Threat%2520Protection%7CAbout%
2520Default%2520Packet%2520Handling%2520Options%7C_____0
NEW QUESTION # 18
With the policies configured as shown in this image, HTTP traffic can be sent and received through branch office VPN tunnel.1 and tunnel.2.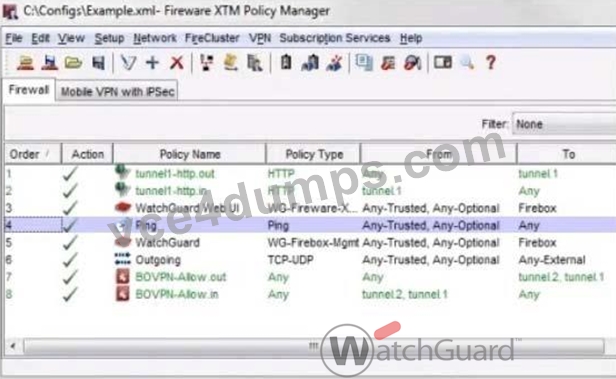
- A. False
- B. True
Answer: A
NEW QUESTION # 19
With the policies configured as shown in this image, HTTP traffic can be sent and received through branch office VPN tunnel.1 and tunnel.2.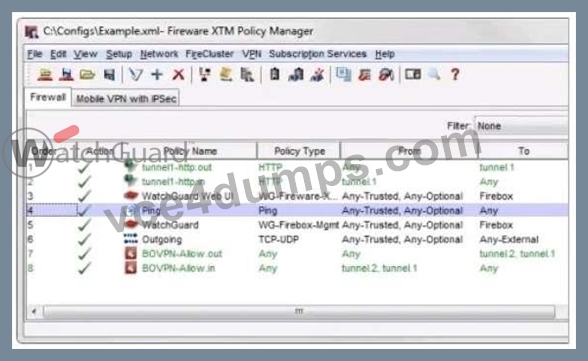
- A. False
- B. True
Answer: A
NEW QUESTION # 20
Which of these options must you configure in an HTTPS-proxy policy to detect credit card numbers in HTTP traffic that is encrypted with SSL? (Select two.)
- A. Data Loss Prevention
- B. Gateway AntiVirus
- C. Application Control
- D. WebBlocker
- E. Deep inspection of HTTPS content
Answer: A,E
NEW QUESTION # 21
Match each WatchGuard Subscription Service with its function.
Uses signatures to provide real-time protection against network attacks. (Choose one).
- A. APT Blocker
- B. Data Loss Prevention DLP
- C. Intrusion Prevention Server IPS
- D. Application Control
- E. Reputation Enable Defense RED
Answer: C
Explanation:
Explanation/Reference:
Intrusion Prevention Service (IPS) -- As with the other IPS offers, the IPS module is intended to detect and in real time mitigate intrusions coming into a network. This includes a large signature data base that monitors for spyware, SQL injections, cross-site scripting (XSS), and buffer overflows.
Reference: http://www.tomsitpro.com/articles/network-security-solutions-guide, 2-866-6.html
NEW QUESTION # 22
To enable remote devices to send log messages to Dimension through the gateway Firebox, what must you verify is included in your gateway Firebox configuration? (Select one.)
- A. You can only send log messages to Dimension from a computer that is on the network behind your gateway Firebox.
- B. You must make sure that either the WG-Logging packet filter policy, or another policy that allows external connections to Dimension over port 4115, is included in the configuration file.
- C. You must change the connection settings in Dimension, not on the gateway Firebox.
- D. You must add a policy to the remote device configuration file to allow traffic to a Dimension.
Answer: D
NEW QUESTION # 23
If you use an external authentication server for mobile VPN, which option must you complete before remote users can authenticate? (Select one.)
- A. Add the remote users to a Mobile VPN user group on your Firebox.
- B. Reboot the authentication server.
- C. Add the Mobile VPN user group and remote users to your authentication server.
- D. Create aliases for each remote user's virtual IP address.
Answer: C
NEW QUESTION # 24
Match the monitoring tool to the correct task.
Which tool can learn the status of your IPS signature database? (Select one)
- A. Log Server
- B. FireWatch
- C. Firebox System Manager - Subscription services
- D. Traffic Monitor
- E. FireBox System Manager - Blocked Sites list
- F. Firebox System Manager - Authentication list
Answer: C
Explanation:
Explanation/Reference:
To look up information about an IPS signature:
1. Open Firebox System Manager.
2. Select the Subscription Services tab.
3. In the Intrusion Prevention section, click Show.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, pages 15, 34, 59, 181
NEW QUESTION # 25
When your device is in a default state, to which interface do you connect your management computer so you can use the Quick Setup Wizard or Web Setup Wizard to configure the device? (Select one.)
- A. Console interface
- B. Interface 0
- C. Interface 1
- D. Any interface
Answer: C
Explanation:
To start the Web Setup Wizard, connect your computer to interface number 1 of your XTMdevice with an Ethernet cable. This is the trusted interface.
Reference:http://www.watchguard.com/help/docs/wsm/xtm_11/en-US/index.html#en-US/installation/qsw_web_about_c.html
NEW QUESTION # 26
Which tool can add an IP address for the Firebox to permanently block? (Select one)
- A. Log Server
- B. FireBox System Manager - Blocked Sites list
- C. FireWatch
- D. Firebox System Manager - Subscription services
- E. Traffic Monitor
- F. Firebox System Manager - Authentication list
Answer: B
Explanation:
Explanation/Reference:
Block a site permanently
The Successful Company network administrator has been driven to distraction recently by a script kiddy using addresses in the 192.136.15.0/24 network to run probes of the Successful network. In this exercise, we permanently block all connections from that network.
1. From Policy Manager, select Setup > Default Threat Protection > Blocked Sites.
The Blocked Sites Configuration dialog box opens.
2. On the Blocked Sites tab, click Add.
3. The Add Site dialog box opens. 3. Use the Choose Type drop-down list to select Network IP. In the Value text box, type 192.136.15.0/ 24.
4. Click OK.
The entry appears in the Blocked Sites list. With this configuration, the Firebox blocks all packets to and from the 192.136.15.0/24 network range.
Reference: Fireware Basics, Courseware: WatchGuard System Manager 10, pages 15, 34, 59, 181
NEW QUESTION # 27
Which authentication servers can you use with your Firebox? (Select four.)
- A. Active Directory
- B. RADIUS
- C. TACACS+
- D. LDAP
- E. Linux Authentication
- F. Kerberos
- G. Firebox databases
Answer: A,B,D,G
Explanation:
Explanation/Reference: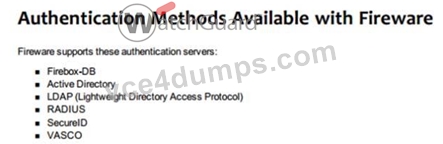
NEW QUESTION # 28
Which takes precedence: WebBlocker category match or a WebBlocker exception?
- A. WebBlocker category match
- B. WebBlocker exception
Answer: B
NEW QUESTION # 29
How can you include log messages from more than one Firebox in a single report generated by Dimension?
(Select two.)
- A. Create a device group and view the reports for that group.
- B. Create a report schedule that includes all the devices you want to include in the report.
- C. Export report data as a single PDF file for all the devices you want to include in the report.
- D. You cannot see report data in Dimension for more than one device.
Answer: A,B
NEW QUESTION # 30
Which of these threats can the Firebox prevent with the default packet handling settings? (Select four.)
- A. Viruses in email messages
- B. Malware in downloaded files
- C. Access to inappropriate websites
- D. IP spoofing
- E. Port scans
- F. Flood attacks
- G. Denial of service attacks
Answer: D,E,F,G
Explanation:
Explanation/Reference:
B: The default configuration of the XTM device is to block DDoS attacks.
C: In a flood attack, attackers send a very high volume of traffic to a system so it cannot examine and allow permitted network traffic. For example, an ICMP flood attack occurs when a system receives too many ICMP ping commands and must use all of its resources to send reply commands. The XTM device can protect against these types of flood attacks: IPSec, IKE, ICMP. SYN, and UDP.
E: When the Block Port Space Probes (port scans) and Block Address Space Probes check boxes are selected, all incoming traffic on all interfaces is examined by the XTM device.
CG: Default packet handling can reject a packet that could be a security risk, including packets that could be part of a spoofing attack or SYN flood attack
Reference: http://www.watchguard.com/help/docs/wsm/xtm_11/en-US/index.html#en-US/ intrusionprevention/default_pkt_handling_opt_about_c.html%3FTocPath%3DDefault%2520Threat%
2520Protection%7CAbout%2520Default%2520Packet%2520Handling%2520Options%7C_____0
NEW QUESTION # 31
Match each WatchGuard Subscription Service with its function.
Cloud based service that controls access to website based on a site's previous behavior. (Choose one).
- A. Reputation Enable Defense RED
- B. Data Loss Prevention DLP
- C. Application Control
- D. WebBlocker
- E. Quarantine Server
- F. Intrusion Prevention Server IPS
Answer: A
Explanation:
Explanation/Reference:
Reputation Enable Device (RED) is a cloud-based reputation service that controls user's ability to get main access to web malicious sites. Works in concert with the WebBlocker module.
Reference: http://www.tomsitpro.com/articles/network-security-solutions-guide, 2-866-6.html
NEW QUESTION # 32
While troubleshooting a branch office VPN tunnel, you see this log message:
2014-07-23 12:29:15 iked (203.0.113.10<->203.0.113.20) Peer proposes phase one encryption 3DES, expecting AES What settings could you modify in the local device configuration to resolve this issue? (Select one.)
- A. BOVPN Tunnel Route settings
- B. BOVPN Tunnel settings
- C. BOVPN-Allow policies
- D. BOVPN Gateway settings
Answer: D
Explanation:
The WatchGuard BOVPN settings error in this example states phase one encryption. Only the BOVPN Gateway settings can specify phase one settings. BOVPN Tunnel settings specify phase 2 settings.
NEW QUESTION # 33
From the SMTP proxy action settings in this image, which of these options is configured for outgoing SMTP traffic? (Select one.)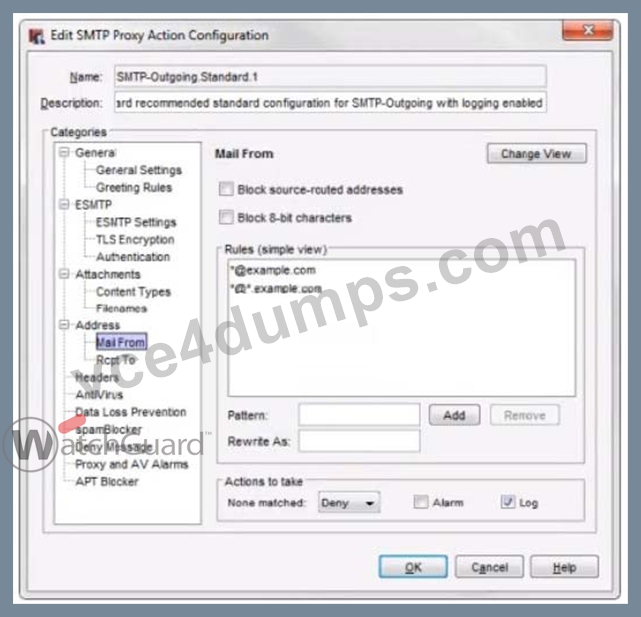
- A. Deny incoming mail from the example.com domain.
- B. Rewrite the Mail From header for the example.com domain.
- C. Deny outgoing mail from the example.com domain.
- D. Prevent mail relay for the example.com domain.
Answer: C
Explanation: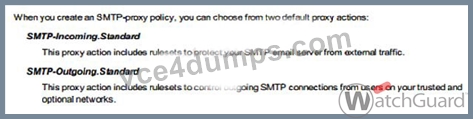
NEW QUESTION # 34
While troubleshooting a branch office VPN tunnel, you see this log message:
2014-07-23 12:29:15 iked (203.0.113.10<->203.0.113.20) Peer proposes phase one encryption 3DES, expecting AES What settings could you modify in the local device configuration to resolve this issue? (Select one.)
- A. BOVPN Tunnel Route settings
- B. BOVPN Tunnel settings
- C. BOVPN-Allow policies
- D. BOVPN Gateway settings
Answer: D
Explanation:
Explanation/Reference:
The WatchGuard BOVPN settings error in this example states phase one encryption. Only the BOVPN Gateway settings can specify phase one settings. BOVPN Tunnel settings specify phase 2 settings.
NEW QUESTION # 35
You need to create an HTTP-proxy policy to a specific domain for software updates (example.com). The update site has multiple subdomains and dynamic IP addresses on a content delivery network. Which of these options is the best way to define the destination in your HTTP-proxy policy? (Select one.)
- A. Configure a host name forupdate.example.com.
- B. Configure an FQDN for*.example.com.
- C. Add IP addresses that correspond to each software update server in the domain.
- D. Create an alias for all subdomains and known IP addresses forexample.com.
Answer: B
Explanation:
http://www.watchguard.com/help/docs/fireware/11/en-US/Content/en-US/policies/fqdn_about_c.html
NEW QUESTION # 36
If your Firebox has a single public IP address, and you want to forward inbound traffic to internal hosts based on the destination port, which type of NAT should you use? (Select one.)
- A. 1-to-1 NAT
- B. Static NAT
- C. Dynamic NAT
Answer: A
NEW QUESTION # 37
In the default Firebox configuration file, which policies control management access to the device? (Select two.)
- A. Outgoing
- B. WatchGuard Web UI
- C. WatchGuard
- D. FTP
- E. Ping
Answer: B,C
Explanation:
Ping is generated by default as the explanation states but Ping does not manage the device. The policies that manage the device are WatchGuard & WatchGuard Web UI
NEW QUESTION # 38
Which authentication servers can you use with your Firebox? (Select four.)
- A. Active Directory
- B. RADIUS
- C. TACACS+
- D. LDAP
- E. Linux Authentication
- F. Kerberos
- G. Firebox databases
Answer: A,B,D,G
Explanation: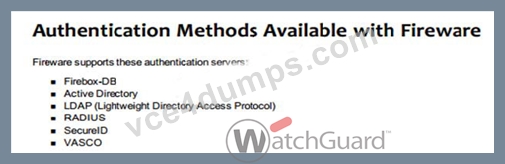
NEW QUESTION # 39
You have a privately addressed email server behind your Firebox. If you want to make sure that all traffic from this server to the Internet appears to come from the public IP address 203.0.113.25, regardless of policies, which from of NAT would you use? (Select one.)
- A. In the SMTP policy that handles traffic from the email server, select the option to apply dynamic NAT to all traffic in the policy and set the source IP address203.0.113.25.
- B. Create a global dynamic NAT rule for traffic from the email server and set the source IP address to
203.0.113.25. - C. Create a static NAT action for traffic to the email server, and set the source IP address to
203.0.113.25.
Answer: B
NEW QUESTION # 40
......
Verified Pass Essentials Exam in First Attempt Guaranteed: https://passguide.vce4dumps.com/Essentials-latest-dumps.html